
Latest Articles

You name it, VMware elevates it (CVE-2025-41244)
NVISO has identified zero-day exploitation of CVE-2025-41244, a local privilege escalation vulnerability impacting VMware's guest service discovery features.

Hunting Chromium Notifications
Browser notifications provide social-engineering opportunities. In this post we'll cover the associated forensic artifacts, threat hunting possibilities and hardening recommendations.
MEGAsync Forensics and Intrusion Attribution
MEGAsync forensics can be leveraged to identify exfiltrated files, additional victims and, subsequently, perform attribution.
Covert TLS n-day backdoors: SparkCockpit & SparkTar
This report documents two covert TLS-based backdoors identified by NVISO: SparkCockpit & SparkTar. Both backdoors employ selective interception of TLS…
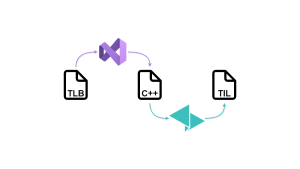
Generating IDA Type Information Libraries from Windows Type Libraries
In this quick-post, we'll explore how to convert Windows type libraries (TLB) into IDA type information libraries (TIL).

IcedID & Qakbot’s VNC Backdoors: Dark Cat, Anubis & Keyhole
In this post we introduce Dark Cat, Anubis and Keyhole, three IcedID & Kakbot VNC backdoor variants NVISO observed. We'll…
Enforcing a Sysmon Archive Quota
This blog post will create a Sysmon archive quota through WMI event consumption to avoid storage exhaustion.
Detecting & Preventing Rogue Azure Subscriptions
In this blog post we will cover why rogue subscriptions are problematic and revisit a solution published a couple of…
Phish, Phished, Phisher: A Quick Peek Inside a Telegram Harvester
In one of the smaller campaigns we monitored last month (September 2021), the threat actor inadvertently exposed Telegram credentials to…
Anatomy and Disruption of Metasploit Shellcode
In April 2021 we went through the anatomy of a Cobalt Strike stager and how some of its signature evasion…